0UTM
For minor breaches (over CLP 350 million)
We audit your cybersecurity and the way you handle data, we leave you evidence and a staged plan to meet what the law requires, and we stay with you through implementation. Built for SMBs, without red tape.
Cybersecurity + Privacy • Law 21,719 • Defensible evidence
Reply within 24h • Built for SMBs • Assessment + executable plan
We work with the international standards used to measure information security and privacy:
For minor breaches (over CLP 350 million)
For serious breaches (over CLP 700 million)
For very serious breaches (over CLP 1.4 billion)
Four services to protect your company and get you compliant, from the assessment through implementation. A clear review for SMB owners: what risk you carry today, what is missing and what to do first, without red tape.
We review your systems and processes, detect gaps and leave you evidence and a plan prioritised by risk. You get a clear report: gaps, a risk matrix and a 30/60/90 plan with priorities.
Focused on personal data: a map of processing activities, privacy gaps and a plan to be ready for an inspection. We turn the law into concrete actions: baseline policies, owners and records to prove due diligence.
We do not just tell you what is missing: we help you implement the controls and improvements that close the gaps. We prioritise by risk and effort so you invest first where risk really drops.
We put policies, procedures and defensible evidence in writing so you can answer clients, audits or inspections: which control exists, who runs it and how it is proven (access, logs, backups, incidents).
Less theory, more clarity: auditable deliverables so you can decide and act fast.
Prioritised risks and gaps + organised evidence (access, backups, logs, continuity and incidents).
Quick wins + a 30/60/90 roadmap, with suggested owners for your internal IT or an external provider.
A simple checklist, short meetings and minimum permissions. We prioritise what is critical, without red tape.
Baseline policies and procedures + defensible evidence to answer clients, audits or inspections.
We do not hand you an endless list. We bring assets, evidence and gaps together to tell you what to do first, by impact and effort.
You do not need a huge team to be protected. We bring high-level practices to your SMB with a simple approach: prioritise what is critical, reduce risk fast and leave you a clear plan to move forward.
We are engineers with experience in cybersecurity, AI and risk management. We work with SMBs that need practical solutions: we help you avoid fraud, unauthorised access and attacks such as ransomware, without slowing down your operation or filling your day with red tape.
Critical first: we fix what lowers your risk the most, with the least effort for your team.
We work with minimum permissions and treat your information confidentially throughout the process.
Our team turns regulation and good practice into concrete actions for your SMB. We organise policies and processes, define responsibilities and leave clear evidence for audits, clients and tenders. The goal: comply without red tape, reduce risk and avoid surprises.
A simple flow to move fast without losing traceability.
Assets, third parties, cloud, on-premise and criticality criteria.
Policies, configurations, access, backups, logging, continuity and response.
Risks with likelihood/impact and quick wins. Less endless list, more action.
We bring assets, evidence and findings together and run them through our audit and compliance engine.
We check the consistency and backing of the evidence, and confirm requirements and gaps before the final report.
A treatment plan, owners and evidence organised for an external audit.
Prioritised findings, organised evidence and a staged plan to move forward without losing traceability.
The new Law 21,719 creates a Data Protection Agency with real power to inspect and impose fines of up to 5,000 UTM (over CLP 350 million) for minor infringements, up to 10,000 UTM for serious ones and 20,000 UTM (over CLP 1.4 billion) or even up to 4% of annual revenue in the most serious cases.
We help you with a practical assessment: prioritised gaps, baseline evidence and a staged plan so you are ready before an inspection.
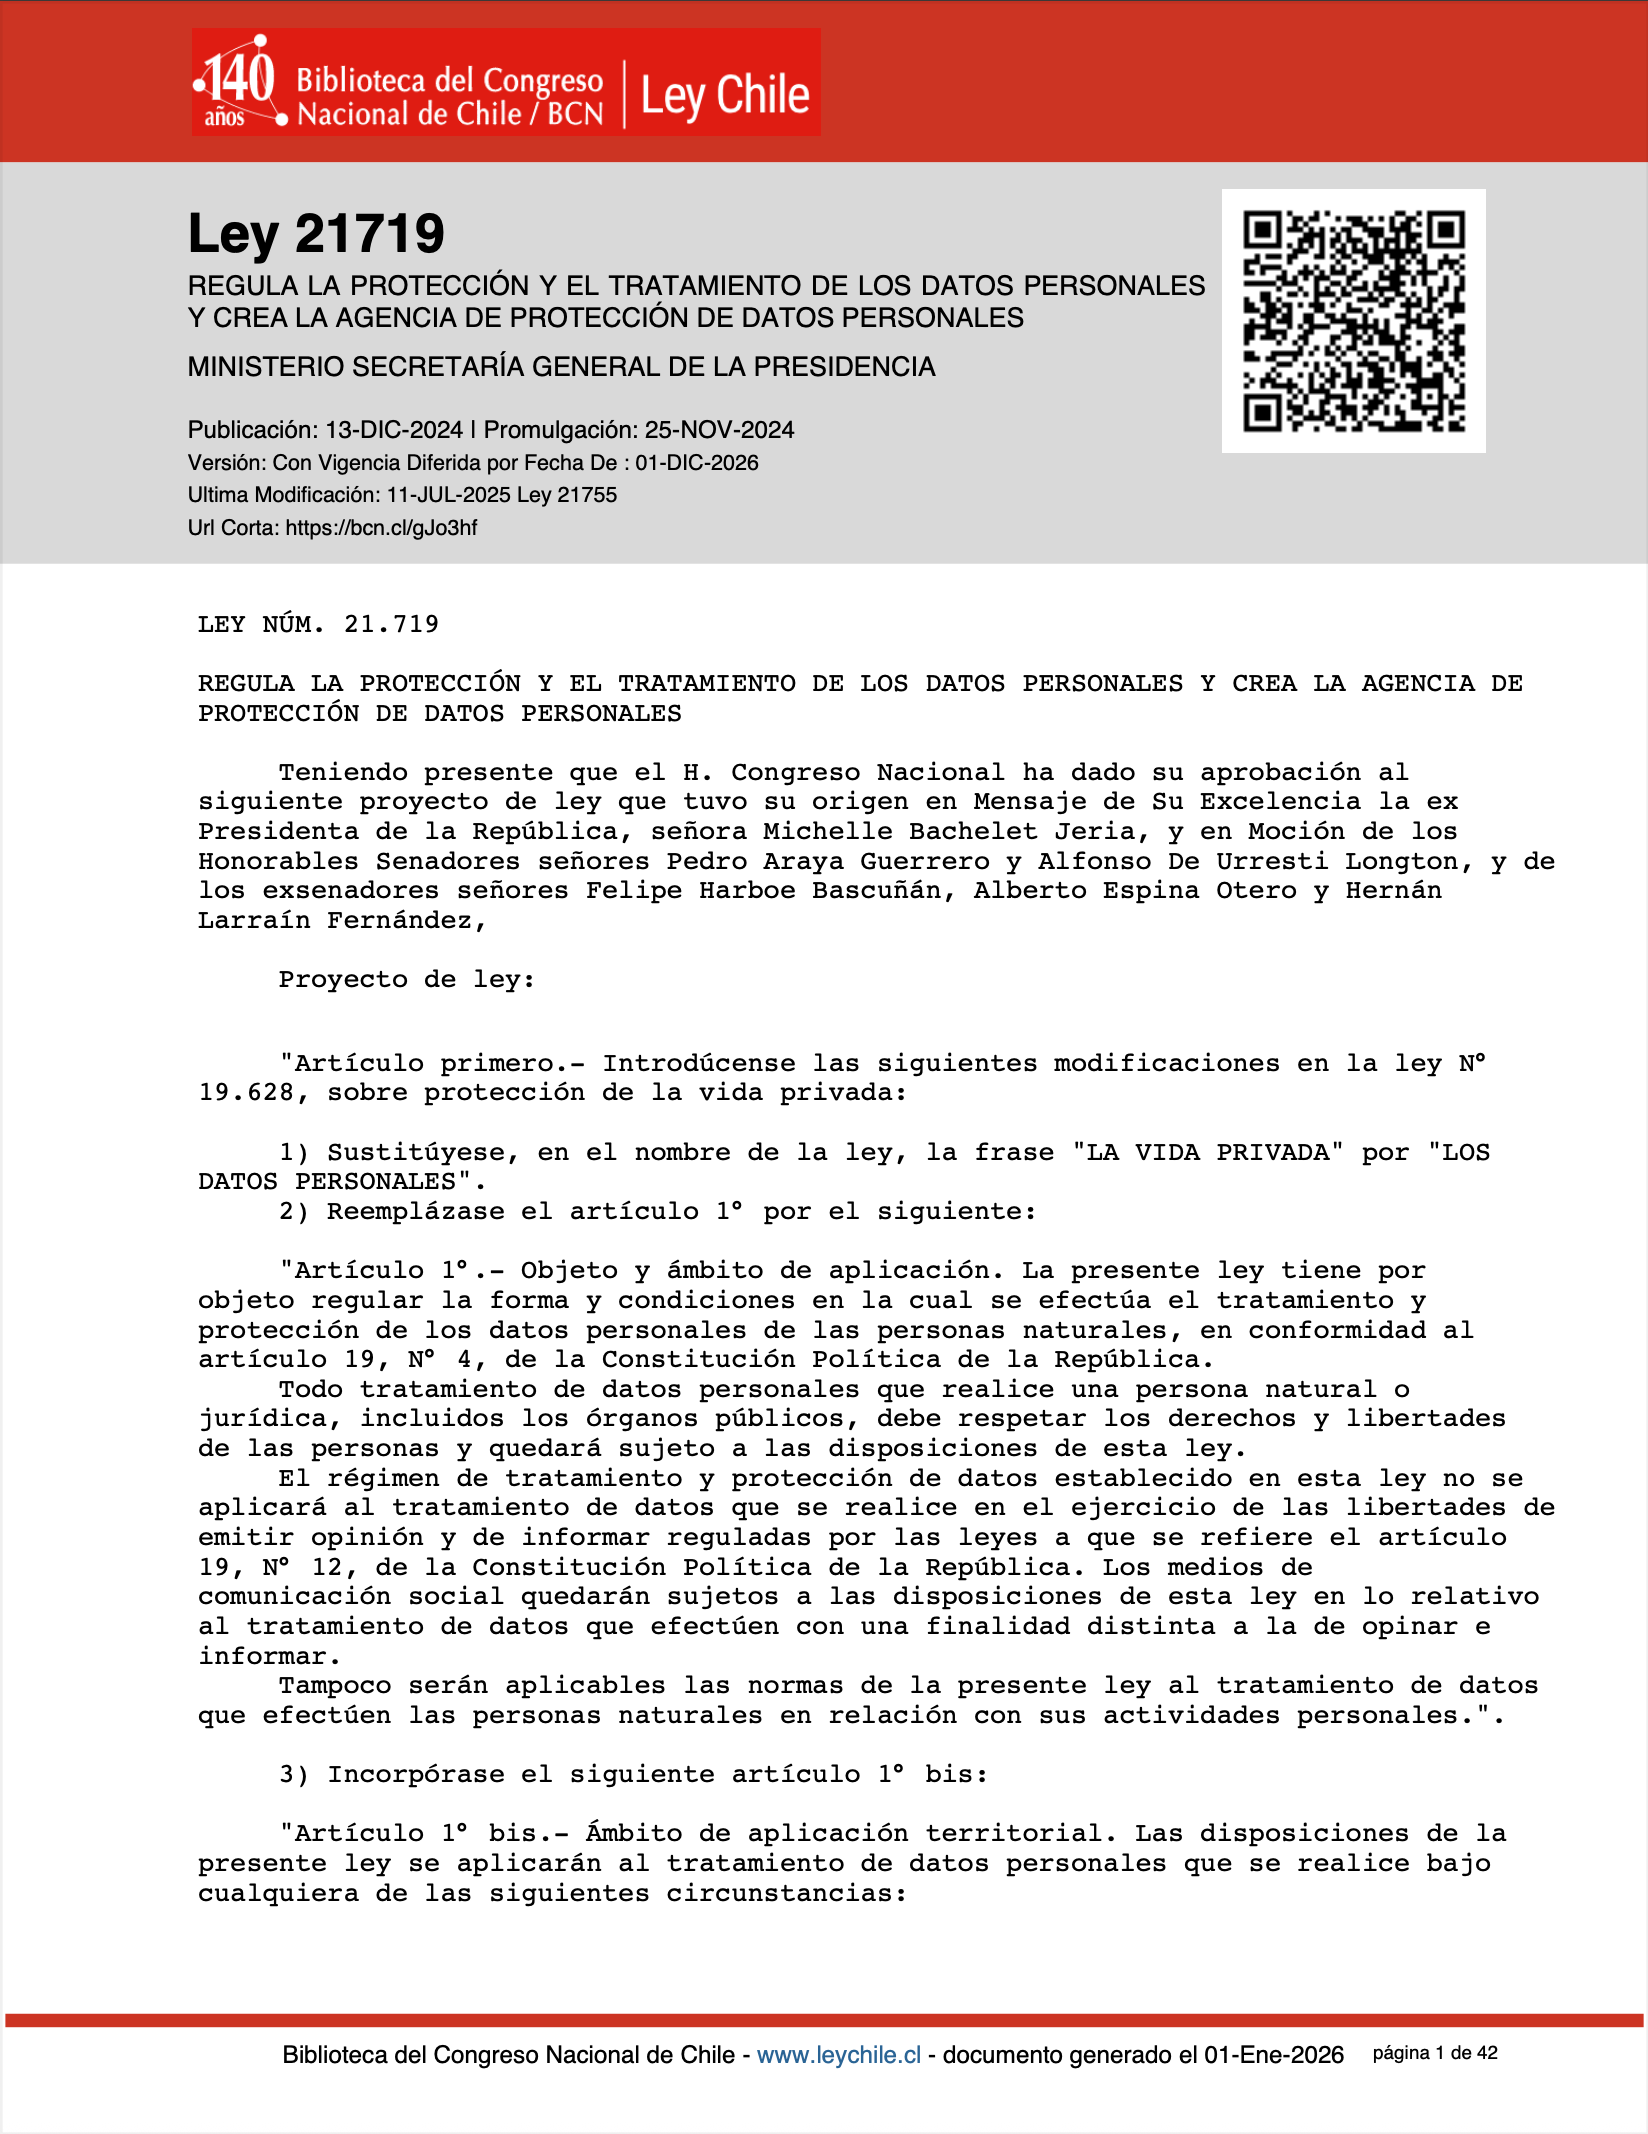
Your audit has to line up with the legal framework and with technical standards. We ground controls and evidence in the Chilean context.
We organise roles, risk management and incident response so that, in an inspection, you can prove due diligence: what you do, who approves it, how you operate and with what evidence.
We strengthen the controls that hold up an investigation: access, logs, retention and evidence preservation. If there is an incident, you reduce uncertainty and respond with verifiable backing.
In an audit for non-compliance, the key is proving control. We define policies, measures and evidence for the personal data lifecycle: classification, access, encryption where it applies and incident procedures, focused on traceability and the requirements of the law.
Your trust is our foundation. Novas Metrics is built with a deep commitment to data privacy and security.
Typical models. We reply within 24h with a proposed scope.
Everything above plus:
A preventive audit is a cost you plan for, once, and it also puts your operation in order. A single very serious fine starts above CLP 1.4 billion, without counting surcharges, suspension and reputational damage. Getting ready is an expense you control; the fine is a loss you do not.
Direct links to the main pages.
What we review, which deliverables you get and how we prioritise by risk.
Compare Cybersecurity and Law 21,719 Compliance: timelines and scope.
Practical context: cybersecurity, personal data and compliance.
Quick answers about scope, deliverables, timelines and confidentiality.
Tell us your context and we reply within 24h.
We reply within 24h with a proposed scope tailored to your company.